API Documentation
API reference for ProcessMind: endpoints, authentication, and integration guides for developers.
To integrate with ProcessMind’s API, you need to create and manage API keys. Learn how to generate, use, and secure your API keys.
In the settings of your ProcessMind account, navigate to the “API Keys” section. Here, you can create a new API key by clicking the New Environment API Key button. Name your key to identify it later.
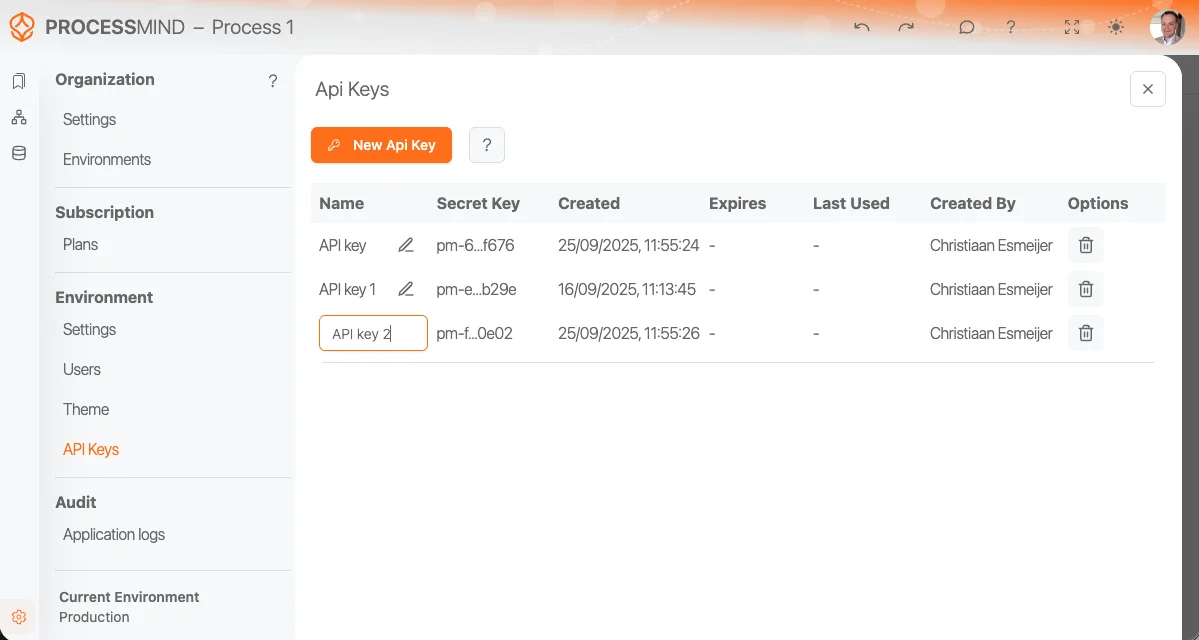
You can create multiple API keys for different applications or services. Each key can be managed independently, allowing you to revoke keys as needed without affecting other integrations. Once the key is generated, copy and store it securely. For security reasons, the key will only be displayed once during creation.
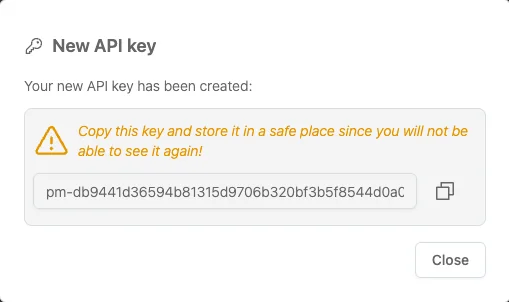
warning
Keep your API keys secure and never expose them in client-side code or public repositories. If a key is compromised, revoke it immediately and generate a new one.
Organization admins can also create organization API keys on the same page. Unlike environment keys, an organization key works across every environment (tenant) of the organization, so one integration can serve all of them. Use organization keys to:
/v1/tenant/{tenantId}/api-keys)./v1/tenant/{tenantId}/users/{userId}/login-token).| Scope | Grants |
|---|---|
| read | Read tenant data (list/get endpoints). On by default. |
| write | Create, update and delete tenant data. On by default. |
| uploadData | Request presigned upload URLs for datatables. On by default. |
| sessions | Mint one-time login handoff tokens. Off by default. |
Enable sessions only for keys that need login handoff, and treat those keys like passwords: a minted token logs the user in without a password prompt. An organization key may mint for users of every environment in the organization; an environment key only for users of its own environment.
POST /v1/tenant/{tenantId}/users/{userId}/login-token returns a single-use token (valid for 60 seconds) bound to the user, environment, and organization, plus a url. Send the user’s browser to that URL and they land in ProcessMind with their own session: no email link and no impersonation. Optionally pass a path in the request body to deep-link to a specific page. The key must have the sessions scope, and a user can only be minted for a tenant the key is allowed to serve.
Minting is audited, tightly rate-limited, and immediately blocked when the key is disabled or the user loses access. The token is returned once and never logged.
We use cookies to improve your experience, personalize content, and analyze traffic. By clicking "Accept All," you consent to our use of cookies.